
Time Travel Debugging on IoT Systems
Learn to research IoT vulnerabilities with emulation and Time Travel Debugging, working through a real CVE from emulation to scenario analysis.


What you'll learn
Skills you'll gain
Courses
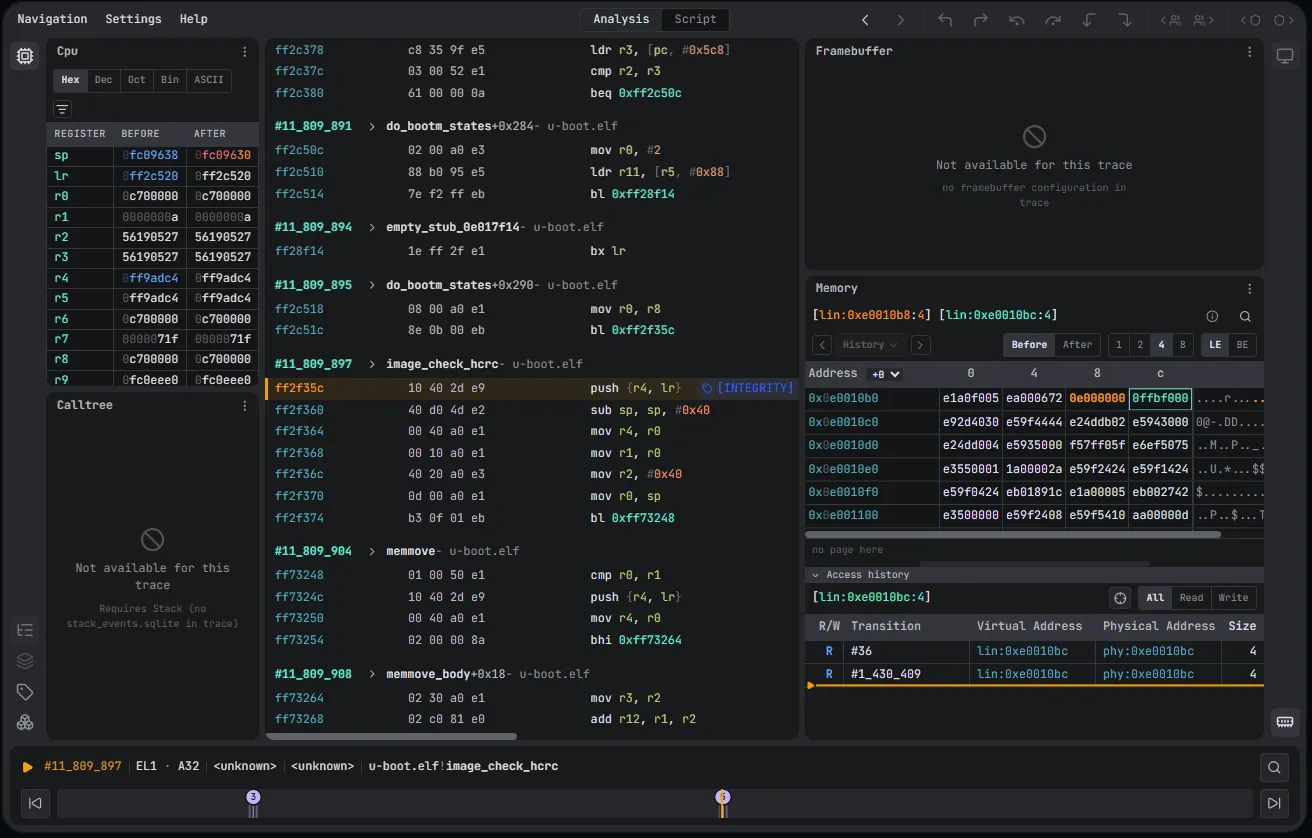
Get hands-on with Time Travel Debugging for IoT vulnerability research, working through a real existing CVE. You'll start by learning about the CVE itself, then manage emulation using the Qiling and Unicorn frameworks. From there, you'll work through the full Time Travel Debugging workflow, including recording, trace generation, and scenario analysis. By the end, you'll be able to confidently apply Time Travel Debugging to practical IoT scenarios.
We adapt every course to your team's level and targets before the session.
Frequently Asked Questions

Share your scope, or even a specific target, and we personalize the session. We select the courses that match your trainees' current knowledge and your objectives, then send you all the information about the training.
No. We give each trainee their own esDynamic account for the training, and everything happens inside it: the theory, the exercises and the wrap-up. It's the same platform your team would use in its daily work.
Three parts: a theory introduction, hands-on exercises in notebooks that trainees work through with the trainer, and a wrap-up where trainees and trainer review every exercise together.
Yes, all of it: slide decks, knowledge notebooks and exercise notebooks. Your team can reuse them in its own esDynamic environment, if you have one.