
Attack your chip before anyone else does
Side-channel analysis, fault injection and firmware testing for teams designing secure chips, IP and SoCs. Run it in your own lab, from the first FPGA prototype to certification, with your designs and results kept in-house.
Security is now part of the spec, and it gets tested
Customers increasingly ask for SESIP, PSA Certified, Common Criteria or FIPS 140-3 before they design a part in. The lab that evaluates it will measure what the chip leaks through its power consumption and try to fault its boot code. Post-quantum algorithms bring new implementations to protect. And a weakness found after tape-out costs a respin, not a code change.
eShard gives your team the platforms to run those same attacks itself: side-channel analysis and fault injection on prototypes and silicon, and fault simulation on firmware before the hardware exists. You find the leak or the fragile branch while it's still cheap to fix, and the results stay inside your organization.
Where this matters for you
Secure IP & crypto cores
If you sell cryptographic or post-quantum IP, your countermeasures are the product. Masking and hiding have to hold up against the attacks an evaluator will run, at first order and beyond, before your IP ends up in someone else's chip.
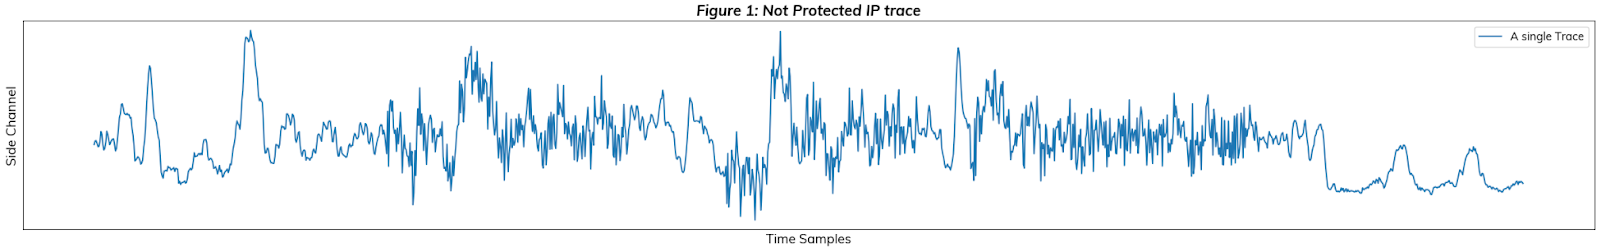
Chips & SoCs
Secure boot, key storage and debug lock all rest on checks that a single well-placed fault can skip. Once the boot ROM is frozen, a fix means a new mask. Testing the boot flow early shows which branches need hardening while that is still a code change.
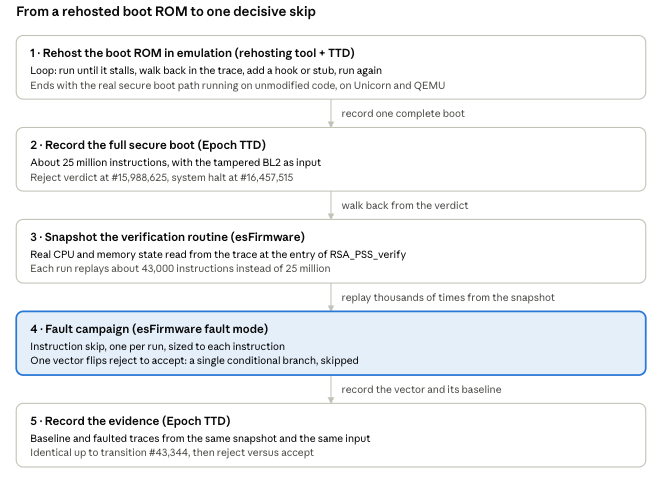
Certification readiness
SESIP, PSA Certified and Common Criteria evaluations at higher assurance levels include physical attacks. Running the same side-channel and fault campaigns in-house, on the kind of platform evaluation labs use, means fewer surprises and fewer rounds once the evaluation starts.
Built for teams whose designs can't leave the building
Everything you need to test your chip in-house
Side-channel analysis
Measure what power consumption and electromagnetic emissions reveal about your keys, from correlation attacks to deep learning at any order, on AES, RSA, ECC and post-quantum algorithms like ML-KEM and ML-DSA.
Fault injection
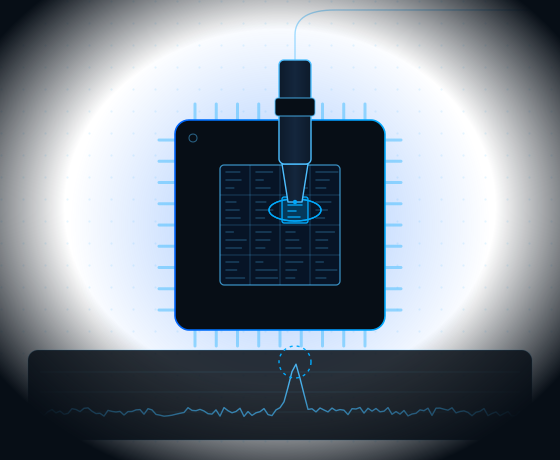
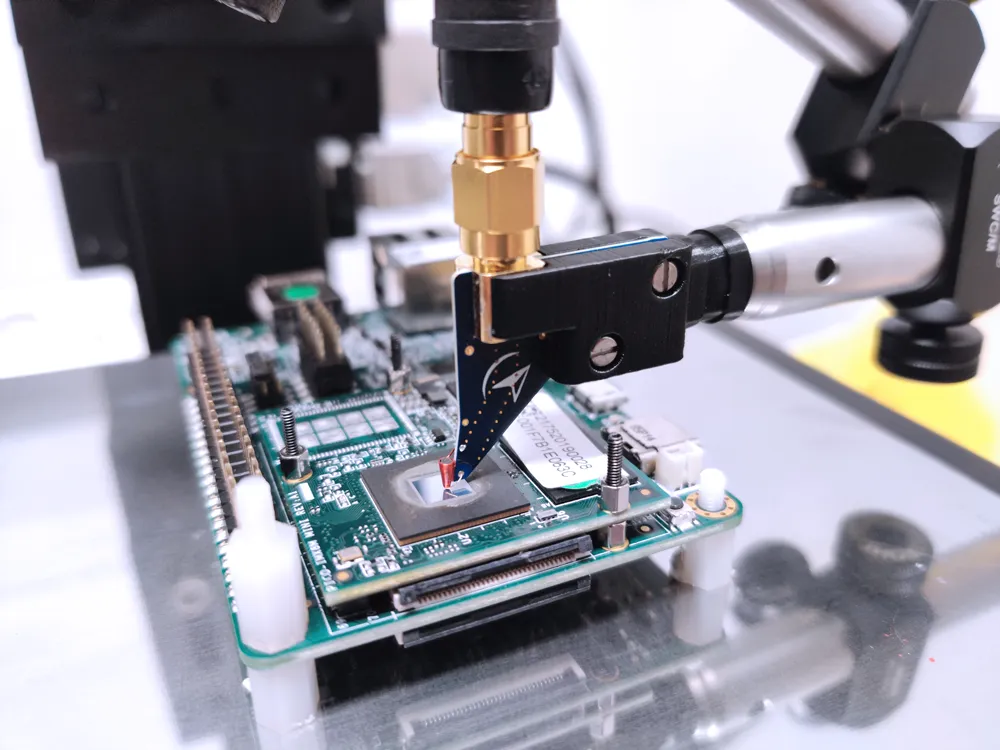
Test how your chip behaves under electromagnetic, laser, and voltage or clock glitching, with spatial mapping, parameter sweeps and backside laser imaging, on the same esDynamic platform as your side-channel work.

Fault simulation
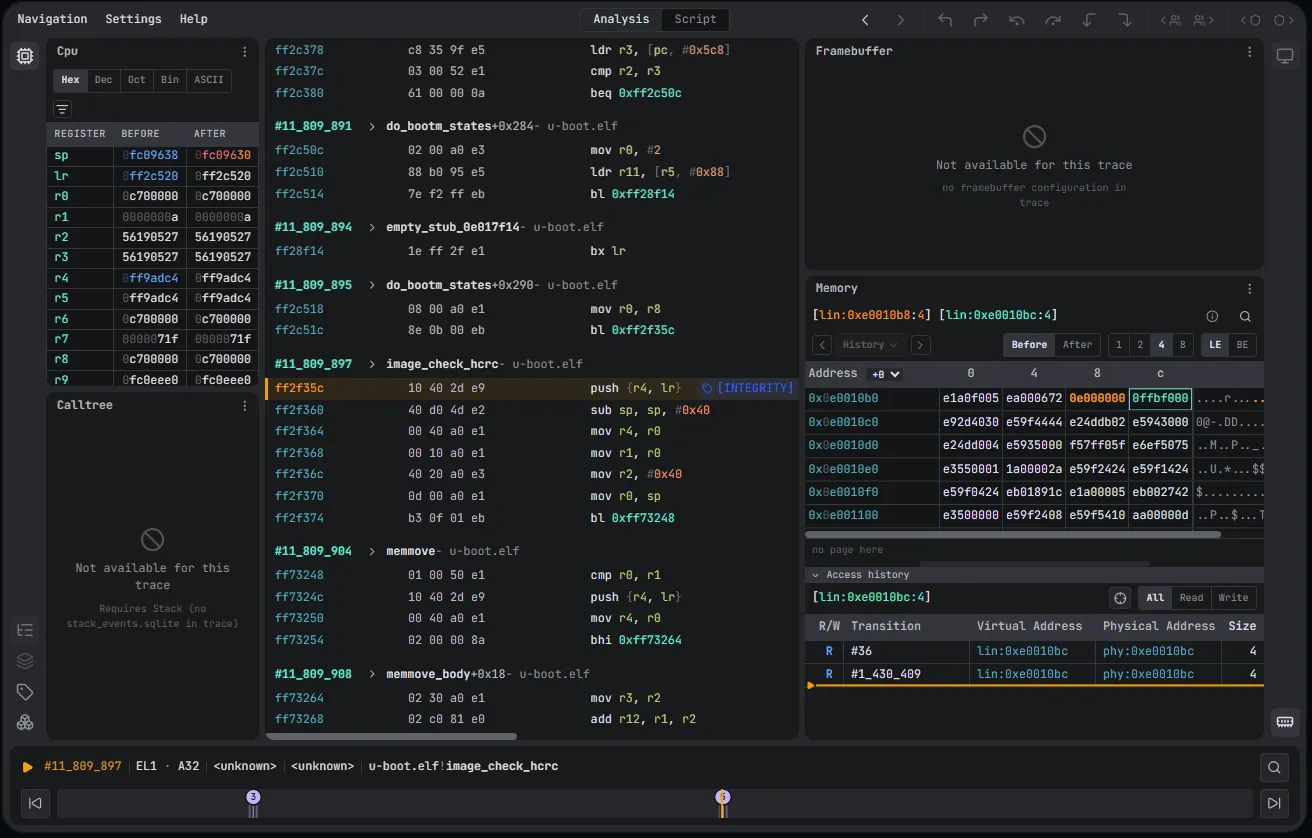
Run boot ROM and firmware in emulation on Arm, Intel or RISC-V, fault it and collect traces before the first sample comes back.
Services
Get results now, build capability for next time
Expert services
Need results before a certification deadline, or a second opinion on a countermeasure? eShard's experts can run the evaluation for you, while your team builds the capability to do it next time.
Request an assessment →esCoaching
Hands-on training built around your chip, your bench and the attacks your evaluation will include, from side-channel fundamentals to post-quantum implementations.
Plan a training →Ready to test your chip in-house?
Tell us about your chip, your certification target and where you want to start. An expert will get back to you.