Security testing that stays under your command
Hardware and software security investigations for teams building and certifying defence, space, aeronautics and government systems. Deployed in your own environment, operated by your own teams, with sensitive assets and results remaining under your control.
Own your security assessment capability
If a device is captured, salvaged or diverted from a supply chain, someone will try to extract what's inside: a key, an algorithm, your software's logic. For defense, space and aeronautics programs, that risk doesn't wait for a scheduled audit.
eShard gives your team the tools and platforms to run that testing itself: side-channel analysis and fault injection on your hardware, reverse engineering on your firmware and operating systems, all under your own roof. The findings and the expertise they build stay inside your organization.
Where this matters for you
Defense
Communications, radar, and autonomous systems all carry the same exposure: cryptographic keys and mission logic embedded in hardware and software that can end up outside your control. What a captured or salvaged device can be made to reveal matters as much as the mission it was built for.
Space
Ground stations, SATCOM systems, and the infrastructure that keeps a space program running spend far more time within reach than anything in orbit does.
That's exactly where hardware and software security testing can happen normally, on a bench, on your own schedule, rather than being treated as a one-shot check before something becomes unreachable.
Aeronautics
Avionics systems often mix hardware that's decades old with newer connected components. A platform built to fly for that long needs security testing that keeps pace with attack techniques that didn't exist when it was designed.
Built for teams that can't outsource their secrets
Everything you need to test in-house
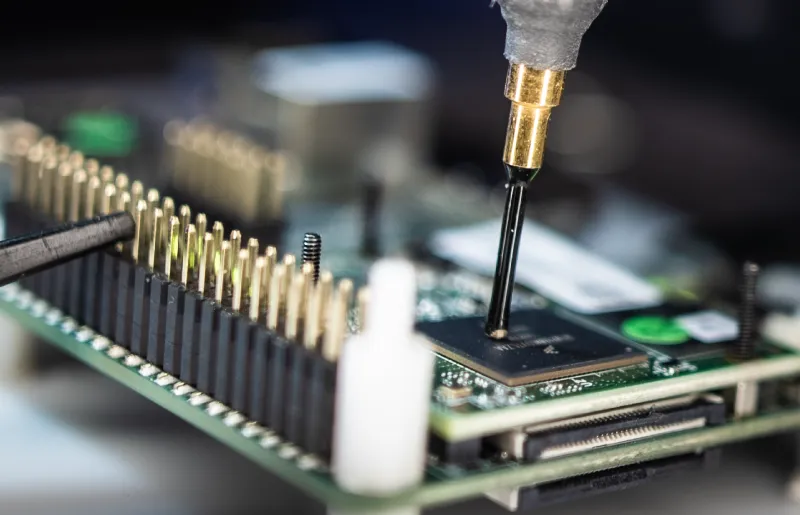
Side-channel analysis
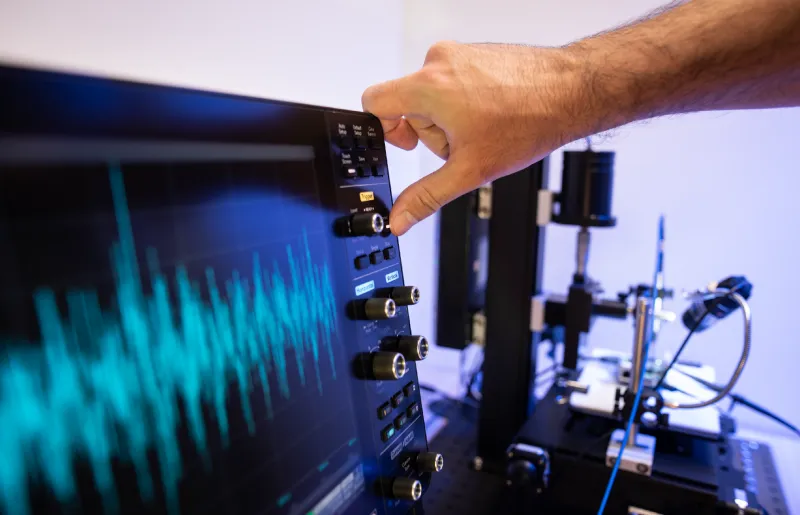
Recover what a device's power consumption or electromagnetic emissions leak about its cryptographic keys, including post-quantum algorithms like ML-KEM and ML-DSA. esDynamic runs the acquisition and analysis on your own bench.
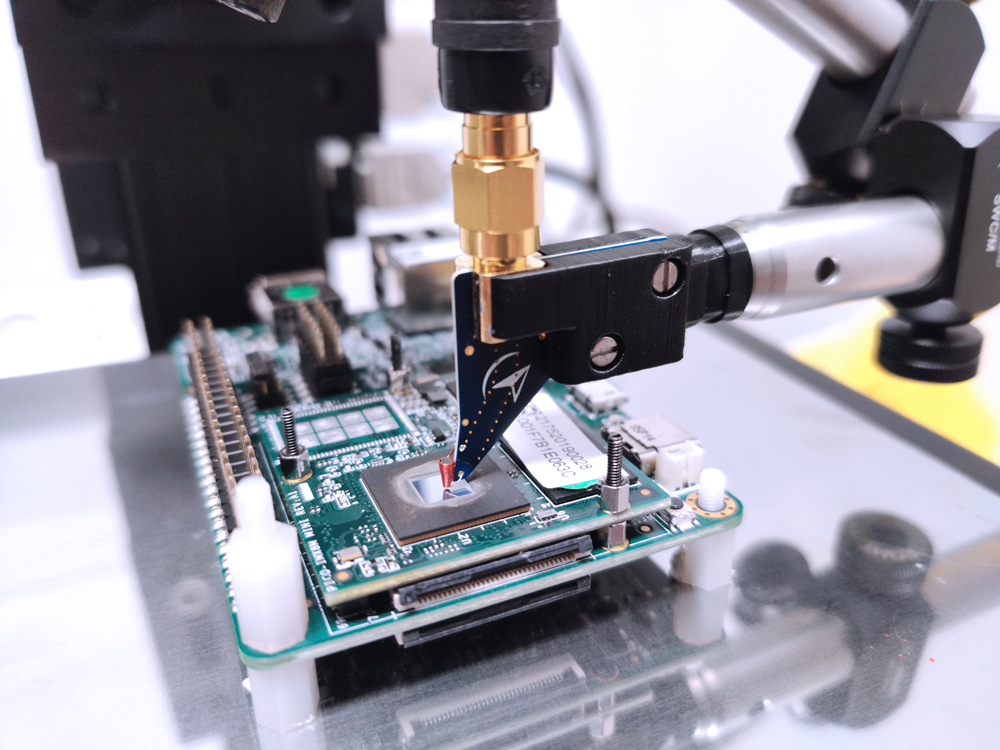
Fault injection
Test how a device behaves under electromagnetic, laser, and voltage or clock glitching attacks, on the same esDynamic platform as your side-channel work.
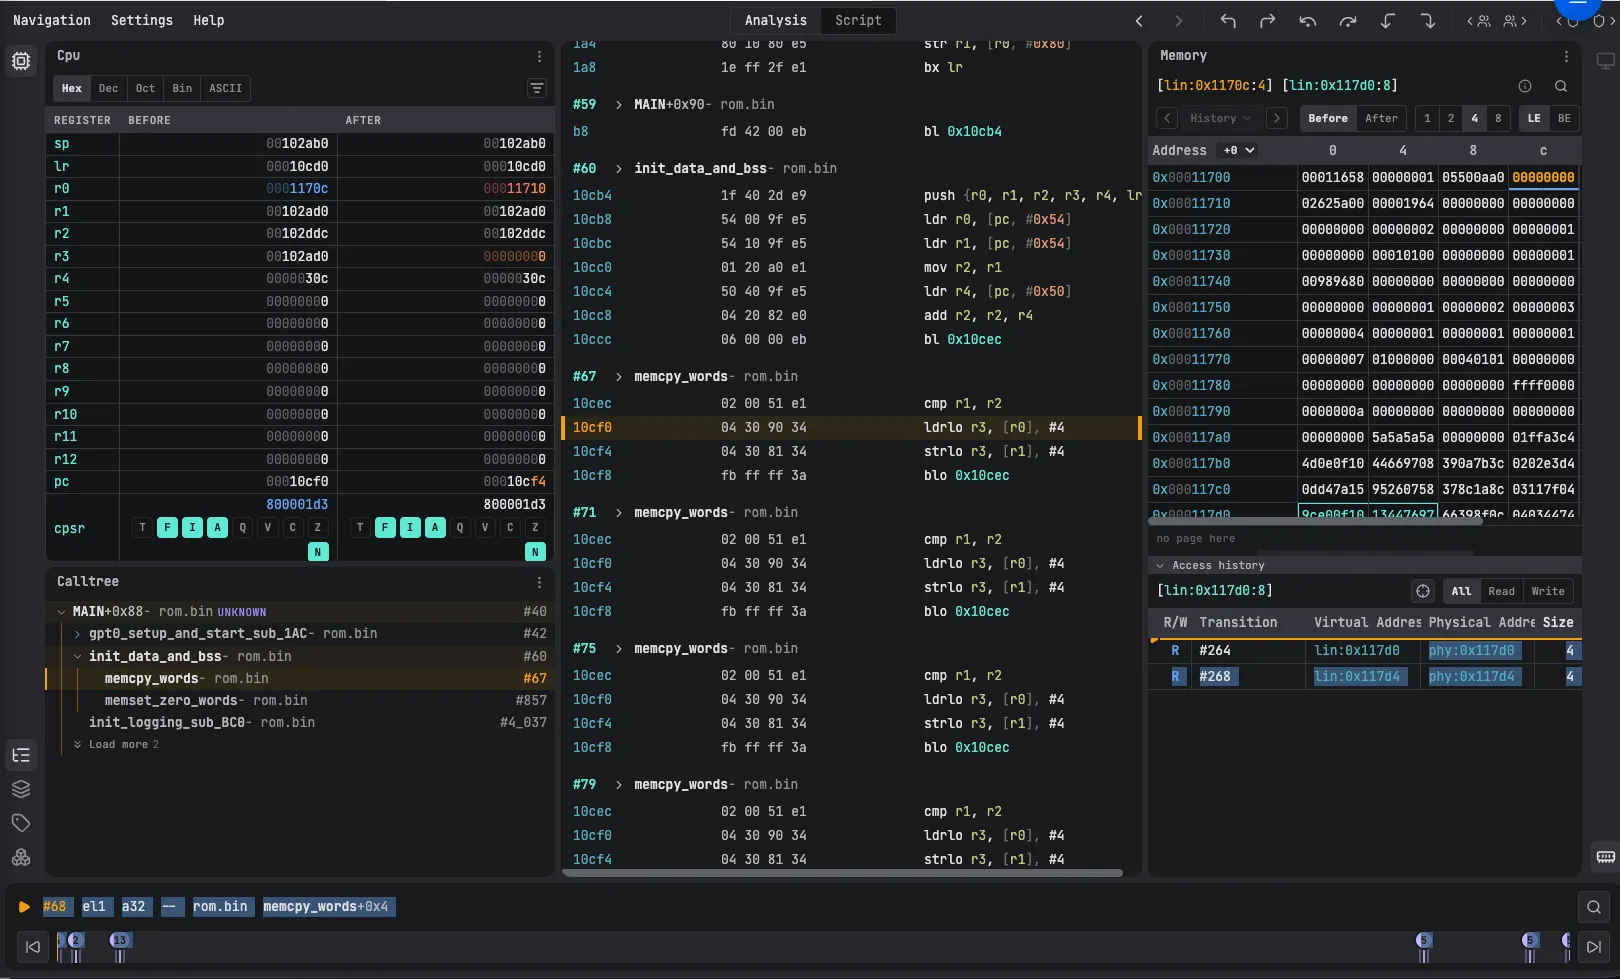
Reverse engineering
Investigate firmware, embedded software, and operating system internals. esReverse and its Epoch time travel debugging engine do the heavy lifting.
Services
Get results now, build capability for next time
Expert services
When you need a specific engagement test and don't have a clearance-ready team in place yet, eShard's experts can run the testing for you. It's a way to get an assessment done now, while you build up in-house capability for next time.
Request an assessment →esCoaching
Hands-on training delivered directly to your team, built around your hardware, your tools, and the specific skills your analysts need next.
Plan a training →Ready to bring security testing in-house?
Talk to our team about your program, your hardware, and where to start.