


Hardware security training
Hands-on trainings in side-channel analysis and fault injection, from your first traces to secret key recovery on real chips. Each one is taught privately to your team and adapted to its level.

Why security teams train with eShard
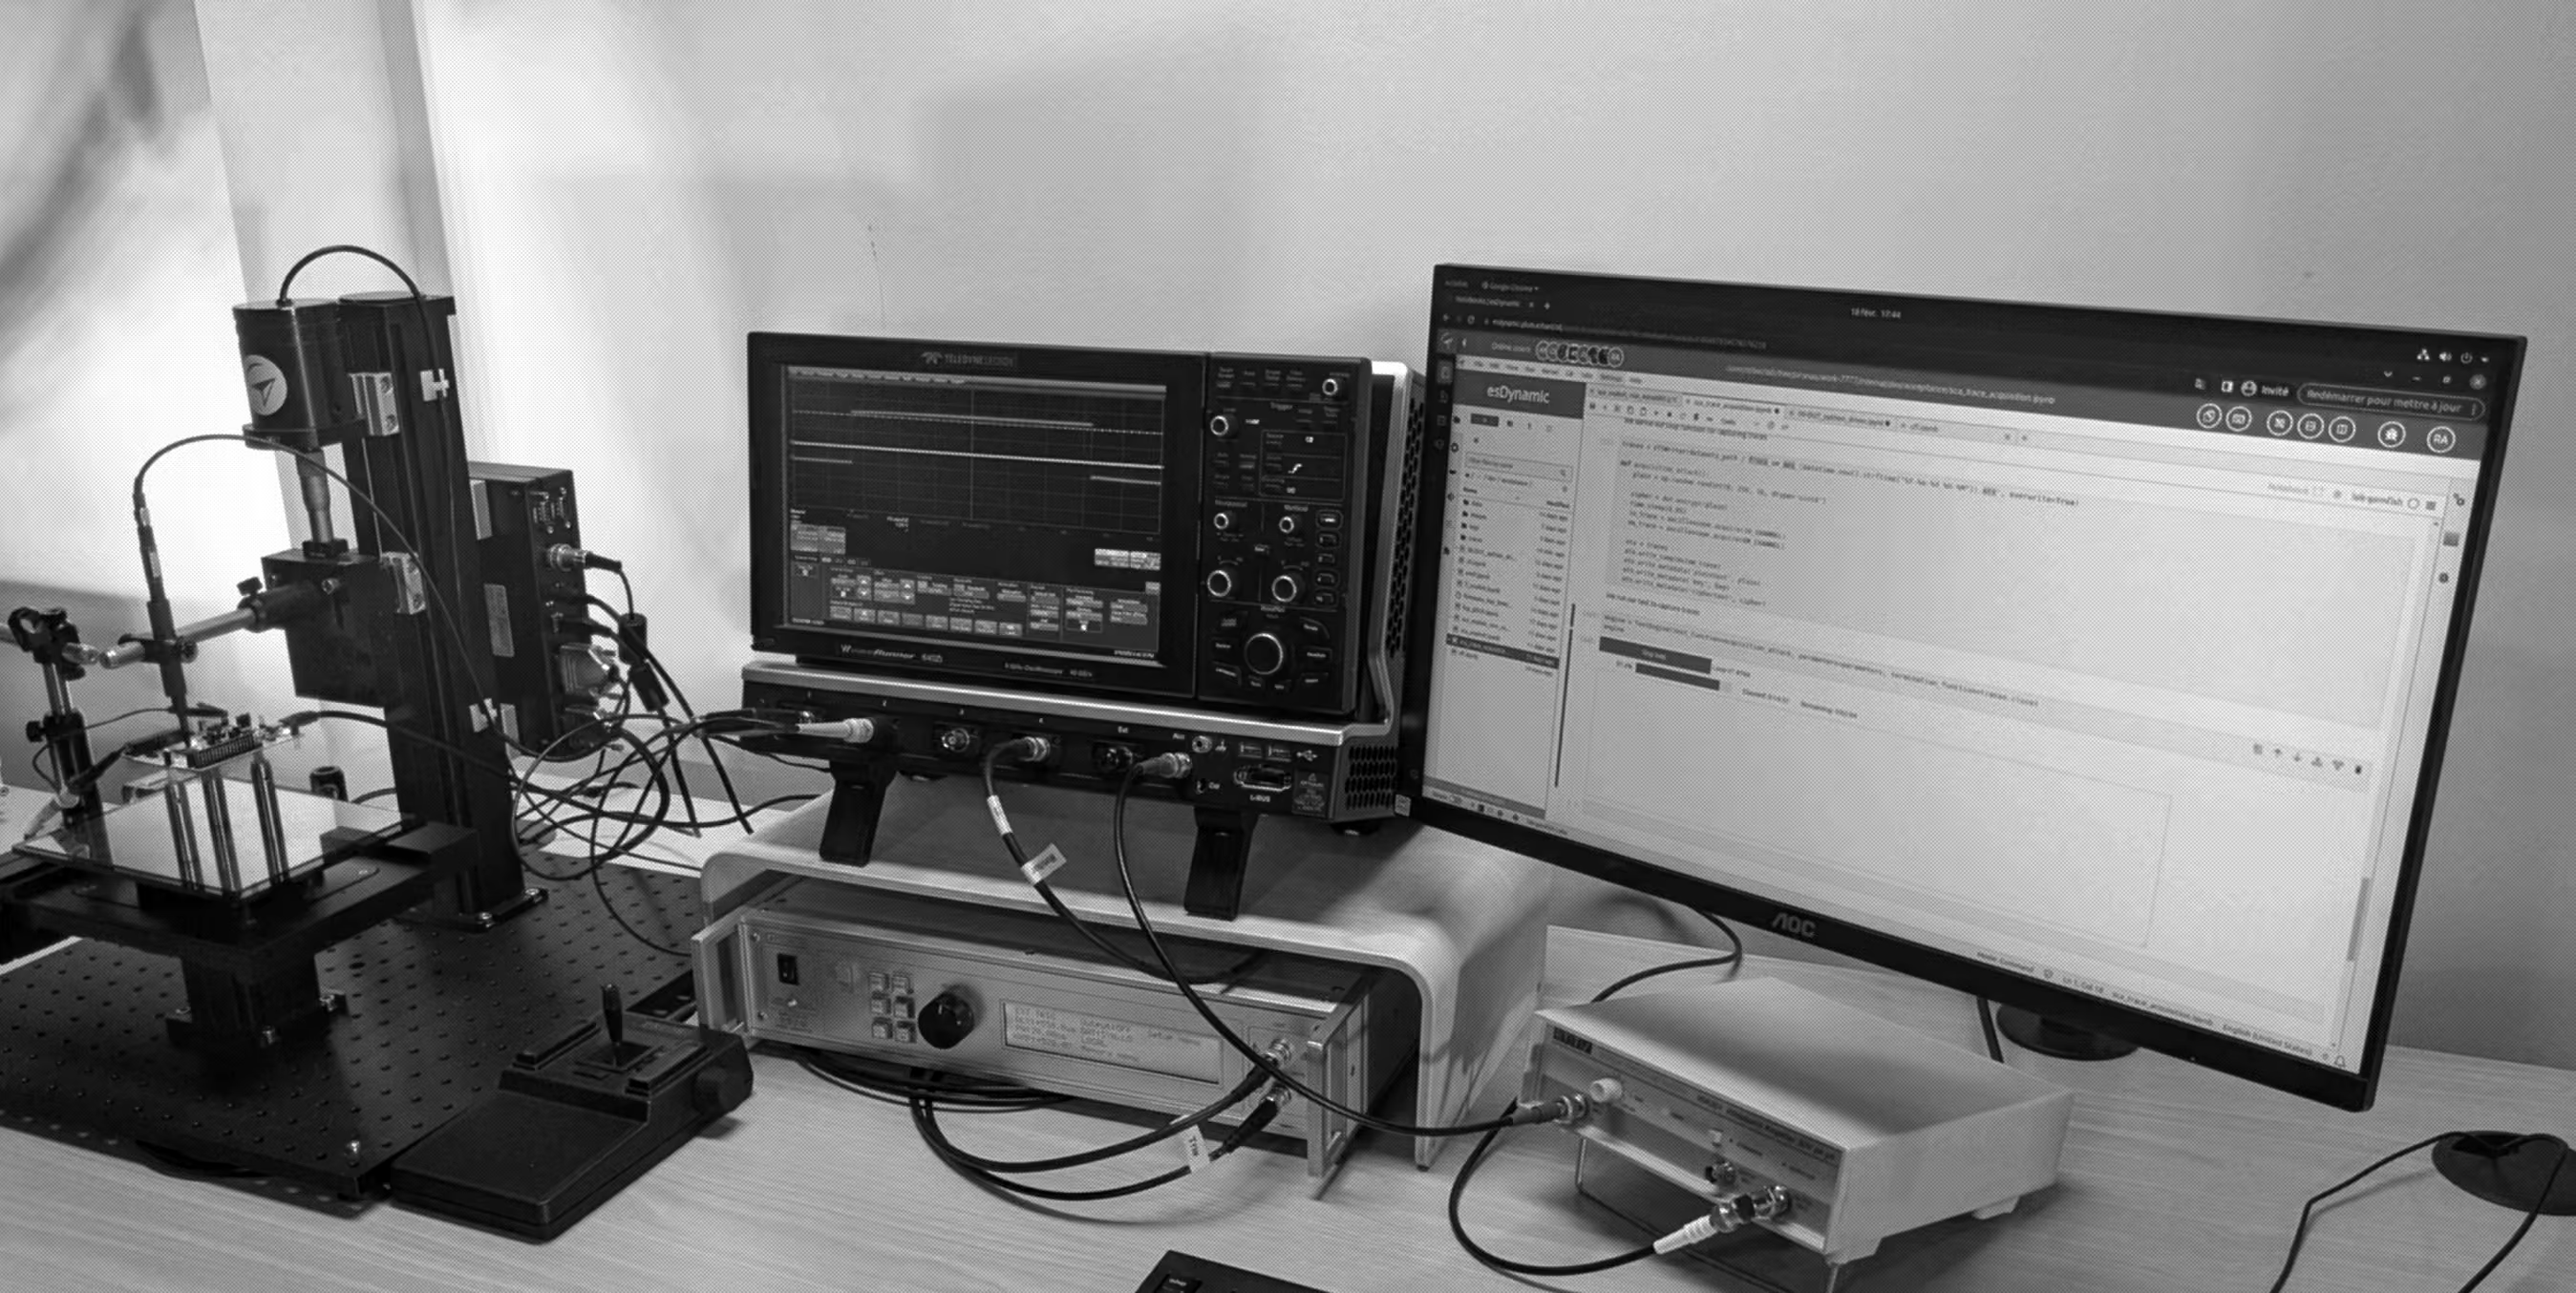
For more than 10 years, eShard engineers have attacked chips and cryptographic implementations in their own side-channel and fault injection labs, for the industry's most demanding security teams. Our trainings pass that experience on to yours.
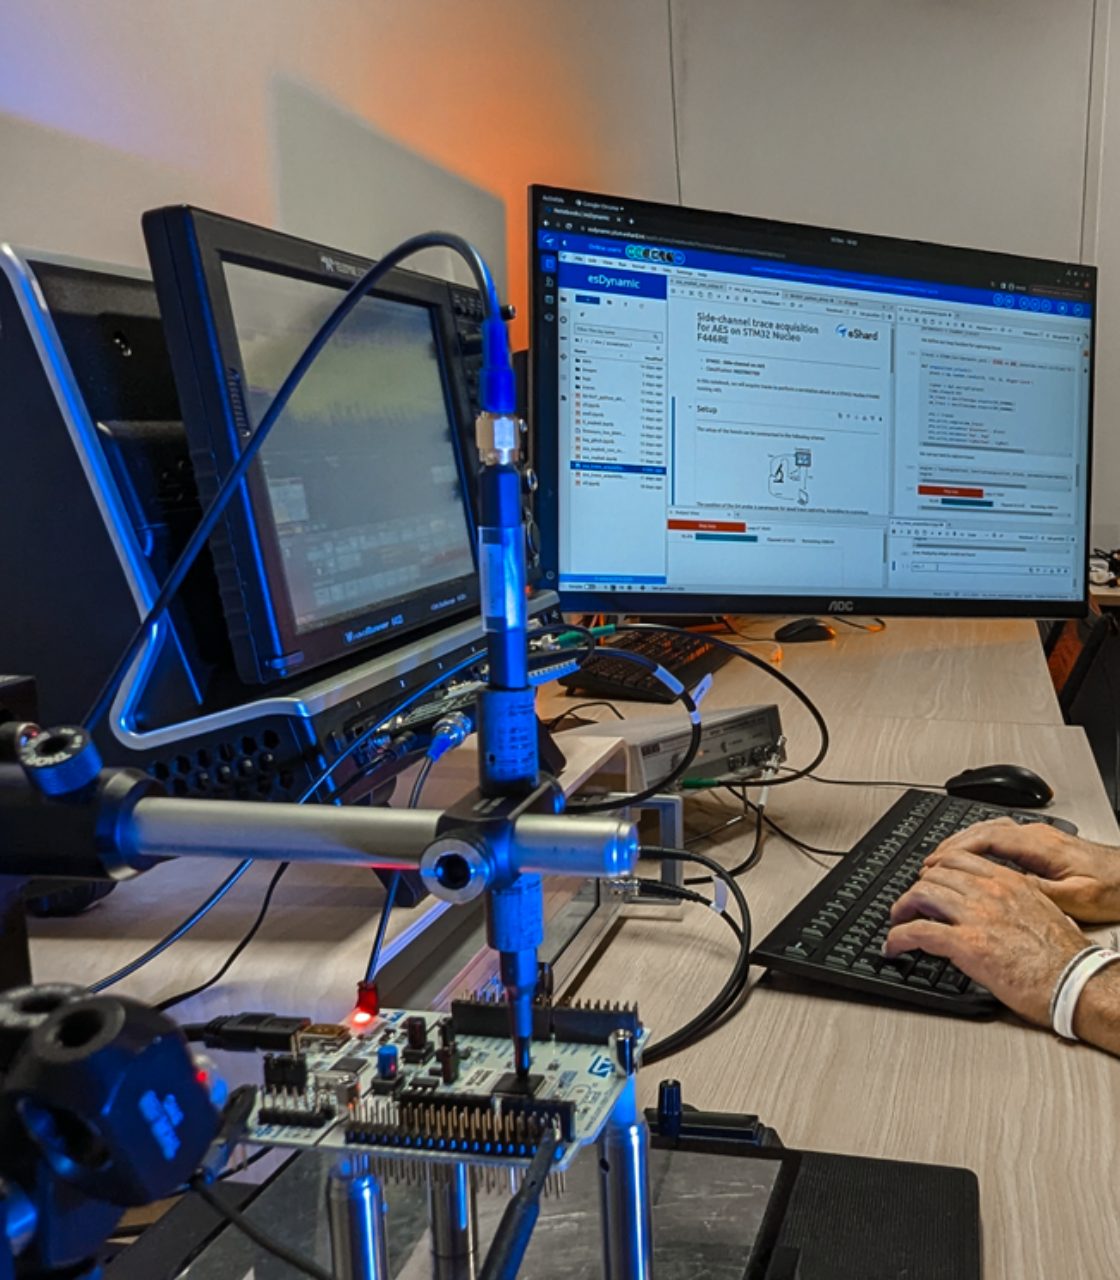

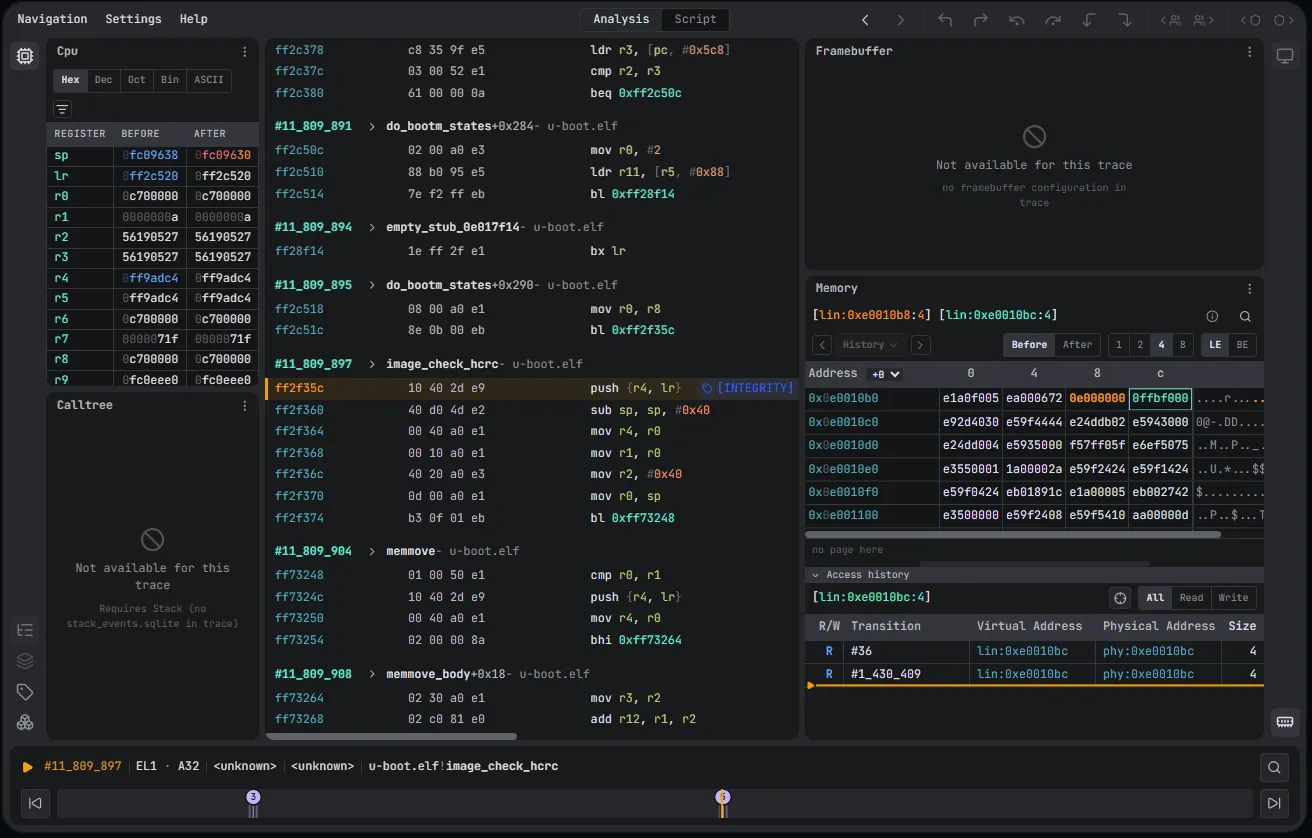
Your trainers are the engineers who build esDynamic, run our side-channel and fault injection labs and publish our research on the blog. They teach what they do every day.

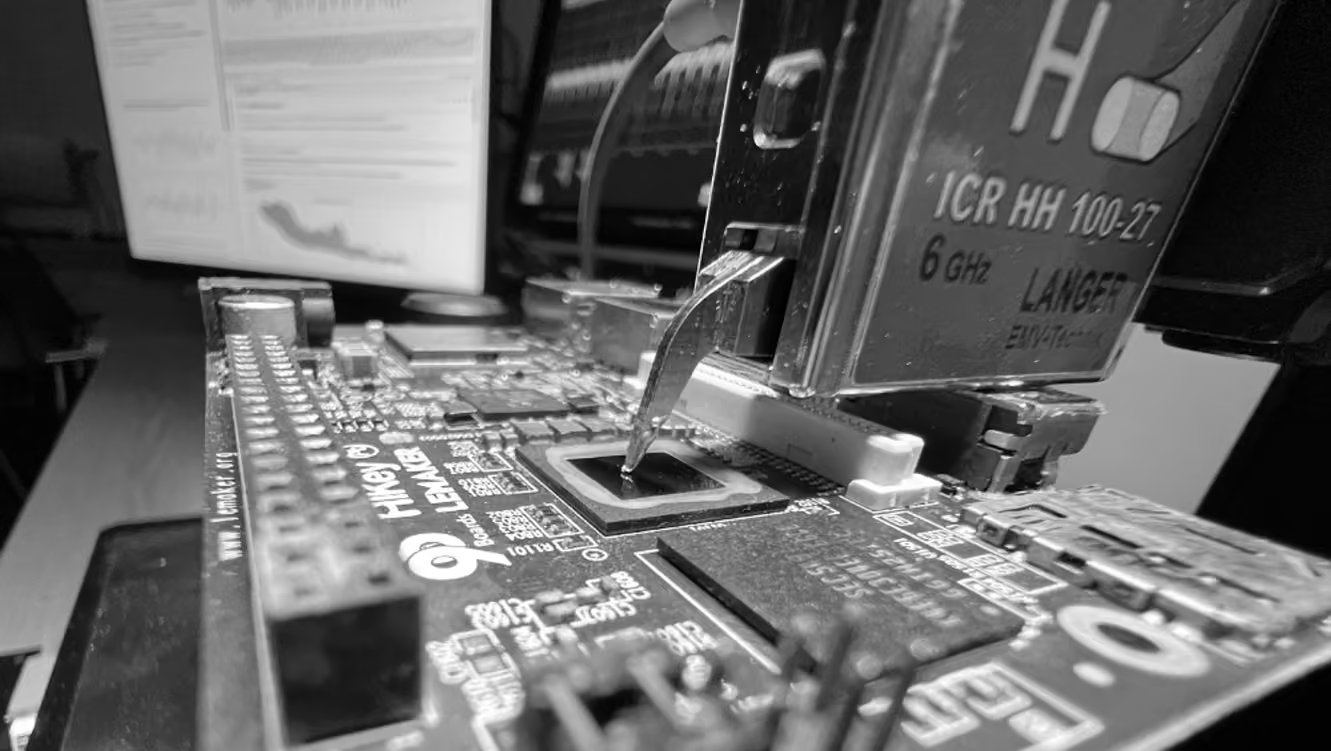
Exercises run on real targets, such as an STM32 with a hardware AES accelerator, an NXP i.MX8 and a Kirin 620 smartphone SoC, and on masked AES including ANSSI's SecAES.

With up to 3 trainees per trainer, each person is guided through every exercise and can bring questions from their own work.


Hands-on coaching sessions built for your team
Tell us about your team and what it needs to learn. An expert will get back to you to shape the sessions with you.
Frequently Asked Questions

Most teams start with Side-Channel Attacks | Essential, which covers the full workflow from trace collection to key recovery. Tell us what your team already does, and we'll suggest where to start.
The fault injection trainings are onsite only, since they run on real benches. The side-channel trainings can be online or onsite. Onsite sessions take place at our office in Bordeaux, France, or at your premises.
Up to 3 trainees per trainer, so everyone moves at the same pace. For a larger team, tell us and we'll plan around it.
Yes. Before the session, we adapt the training to your team's level and, where it helps, to the chips and cryptographic implementations you work on.