
Static Analysis on Windows
Learn to reverse engineer Windows binaries with IDA, Ghidra and Binary Ninja, then work through obfuscation, license protections and real malware.


What you'll learn
Skills you'll gain
Courses
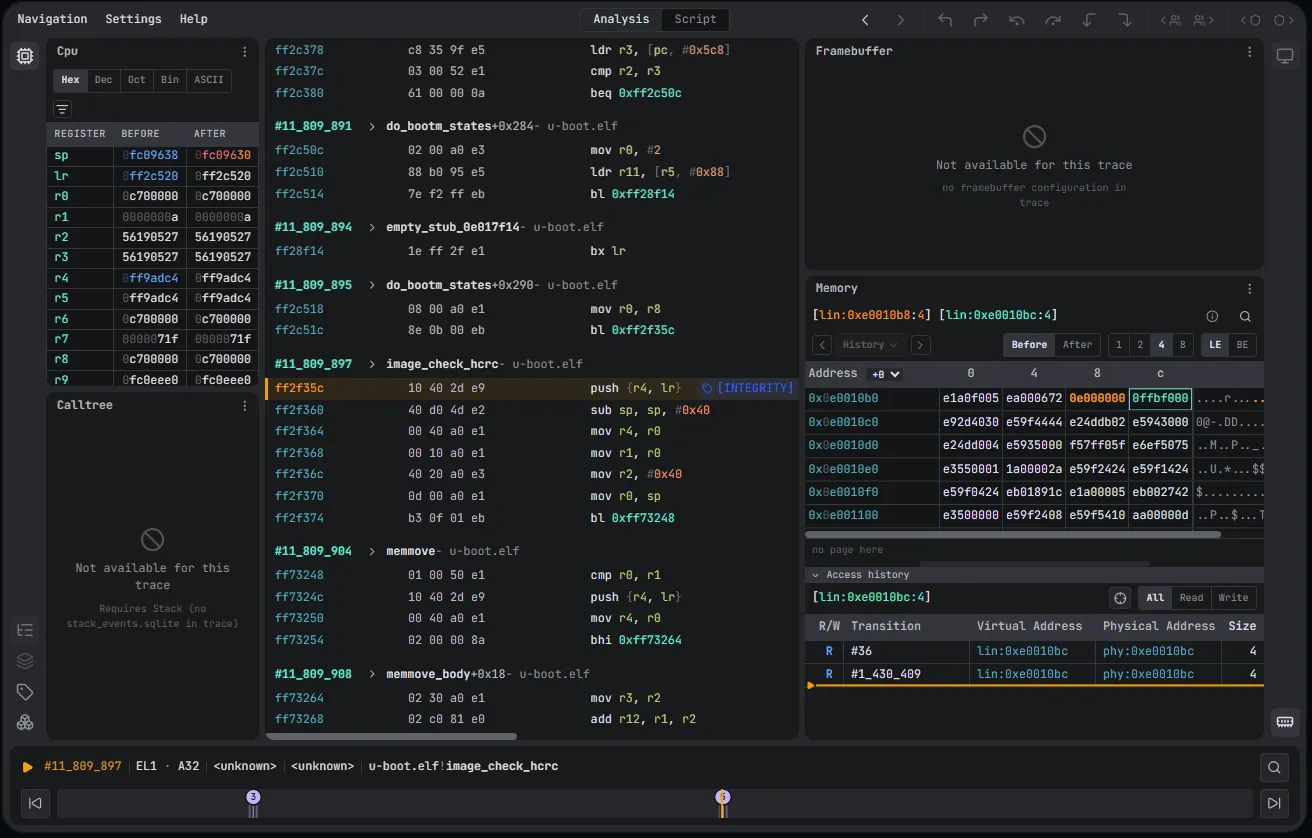
Get hands-on with industry-standard static reverse engineering tools, including IDA, Ghidra, and Binary Ninja. You'll learn to navigate between pseudo-C and assembly representations, and work with core static analysis features such as function graphs, strings, imports and exports, symbols, and cross-references.
Learn to identify and analyze common obfuscation techniques used to hinder static analysis, and how to perform binary patching to work around them.
Apply your skills to real-world targets, including CrackMe challenges, license protection schemes, and malware samples, building the ability to independently perform static analysis of protected and malicious binaries.
We adapt every course to your team's level and targets before the session.
Frequently Asked Questions

Share your scope, or even a specific target, and we personalize the session. We select the courses that match your trainees' current knowledge and your objectives, then send you all the information about the training.
No. We give each trainee their own esDynamic account for the training, and everything happens inside it: the theory, the exercises and the wrap-up. It's the same platform your team would use in its daily work.
Three parts: a theory introduction, hands-on exercises in notebooks that trainees work through with the trainer, and a wrap-up where trainees and trainer review every exercise together.
Yes, all of it: slide decks, knowledge notebooks and exercise notebooks. Your team can reuse them in its own esDynamic environment, if you have one.