
Android Kernel Exploitation: Binder
Learn Android Binder internals, then build a full local privilege escalation exploit for CVE-2023-20938, using Time Travel Debugging to trace and fix it.


What you'll learn
Skills you'll gain
Courses
Master the internals of Android's Binder IPC mechanism, including its core data structures (binder_proc, binder_thread, binder_node), transaction flows, and lifetime management, building the foundation needed for kernel-level exploitation work.
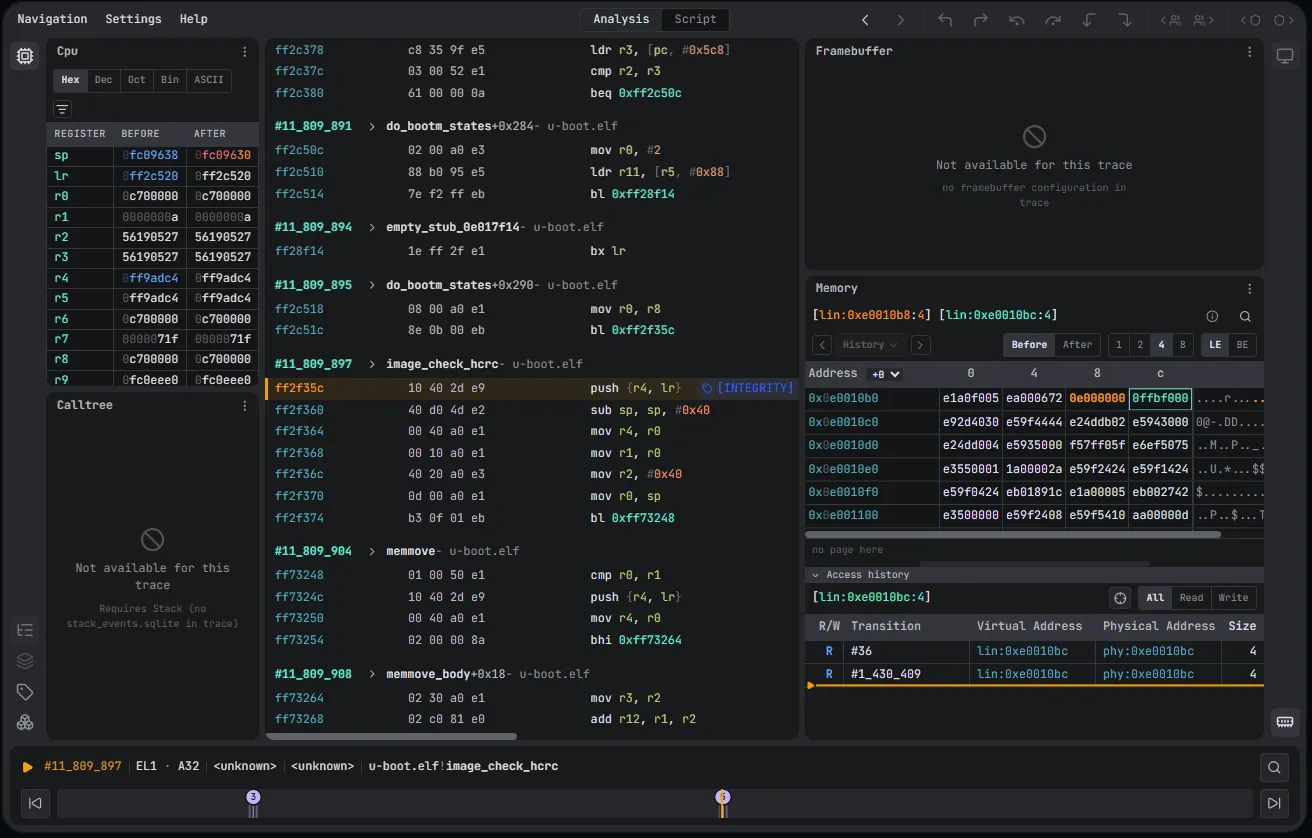
Analyze a real use-after-free vulnerability in the Binder driver, from its root cause in misaligned offsets_size handling to the exploitation primitives it enables, including leaks and arbitrary read/write. Using Time Travel Debugging, you'll trace kernel crashes, reverse-engineer heap states, and debug complex race conditions and double-free scenarios.
Build a complete exploit chain for local privilege escalation: trigger the use-after-free via a two-process Binder setup, craft exploitation primitives such as leaks and arbitrary read/write, and overwrite credential structures to escalate privileges.
Use Time Travel Debugging to stabilize the exploit, identifying and resolving issues such as heap-spray evictions or double-free. The final exploit is validated in a controlled Android 12 (aarch64) emulator environment with vulnerable kernel images.
We adapt every course to your team's level and targets before the session.
Frequently Asked Questions

Share your scope, or even a specific target, and we personalize the session. We select the courses that match your trainees' current knowledge and your objectives, then send you all the information about the training.
No. We give each trainee their own esDynamic account for the training, and everything happens inside it: the theory, the exercises and the wrap-up. It's the same platform your team would use in its daily work.
Three parts: a theory introduction, hands-on exercises in notebooks that trainees work through with the trainer, and a wrap-up where trainees and trainer review every exercise together.
Yes, all of it: slide decks, knowledge notebooks and exercise notebooks. Your team can reuse them in its own esDynamic environment, if you have one.